 VAST VIEW
D-Link Admits It Can't Patch New Zero-Day Flaws Hitting Its DGS-3130 Switches
D-Link is warning customers of multiple unpatched security holes in its DGS-3130 series switches, urging businesses to apply workarounds now since no official fix is available yet.
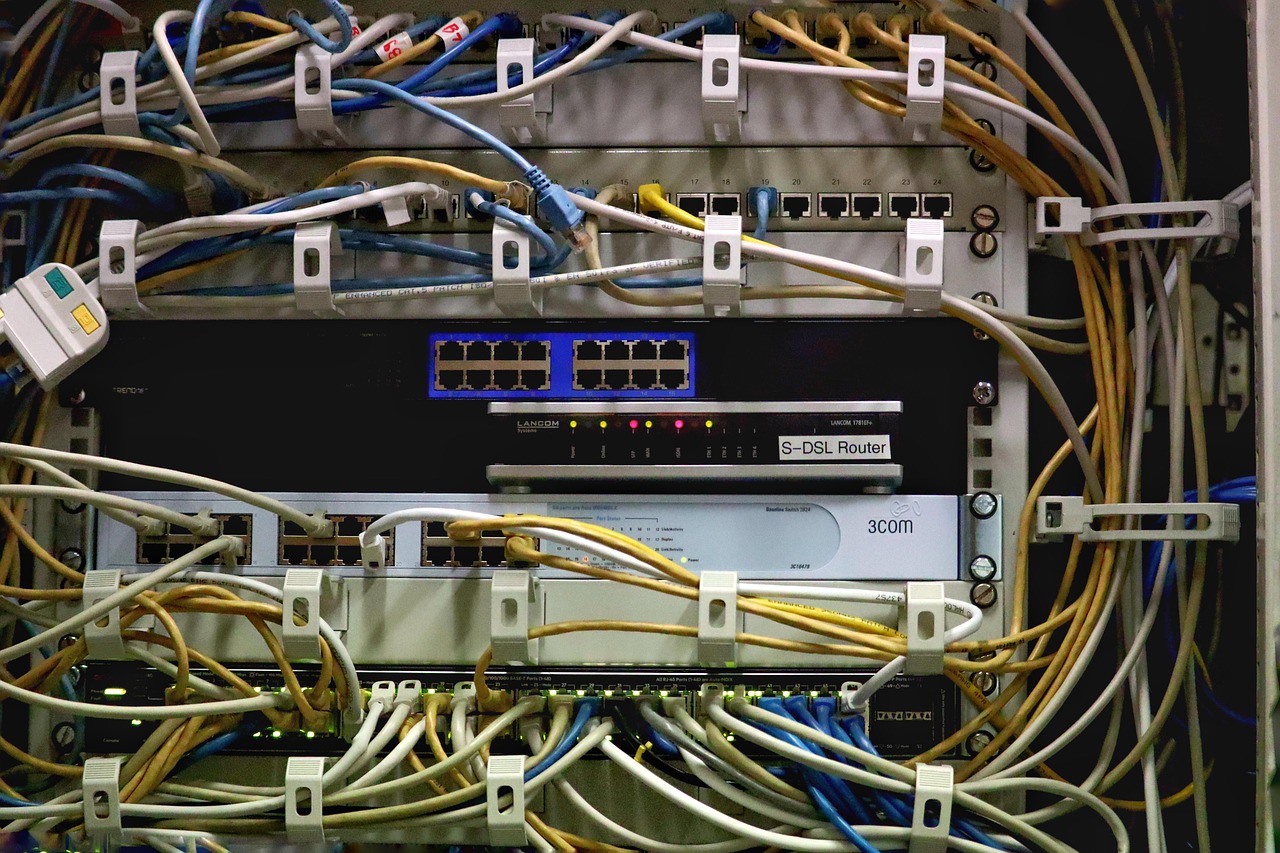
Photo by Tho-Ge via Pixabay
D-Link has issued an alert about several zero-day vulnerabilities affecting its DGS-3130 series managed Gigabit stackable switches, according to BleepingComputer. The flaws remain unpatched, meaning the company currently has no official software fix ready to close the security gaps.
Instead of a patch, D-Link has published mitigation steps designed to help network administrators reduce the risk of exploitation while a permanent solution is developed. These switches are typically deployed in business and enterprise networks, making unaddressed vulnerabilities a potential entry point for attackers targeting organizational infrastructure.
BleepingComputer reports that D-Link is encouraging affected customers to review the recommended precautions immediately, given that the security issues are being disclosed before a fix exists. Organizations running the DGS-3130 series are advised to apply the suggested configuration changes and monitor for further updates from the manufacturer.
Sources: BleepingComputer
More from Cyber
MetaMask moved to calm user fears, confirming that a recent security incident left its wallet infrastructure untouched despite the alarm it triggered.
A botched server migration left an internal DigiCert system wide open to the internet, giving outsiders access to customer records and identity documents, the company confirms.
SonicWall says it won't patch two newly disclosed vulnerabilities in its discontinued Global Management System software, leaving any still-running systems permanently exposed.